01
Microsoft Intune MDM
Full mobile device and application management. Enrollment strategy, compliance policies, configuration profiles, and Conditional Access policy design that survives audit.
MDM / MAMComplianceEntra ID
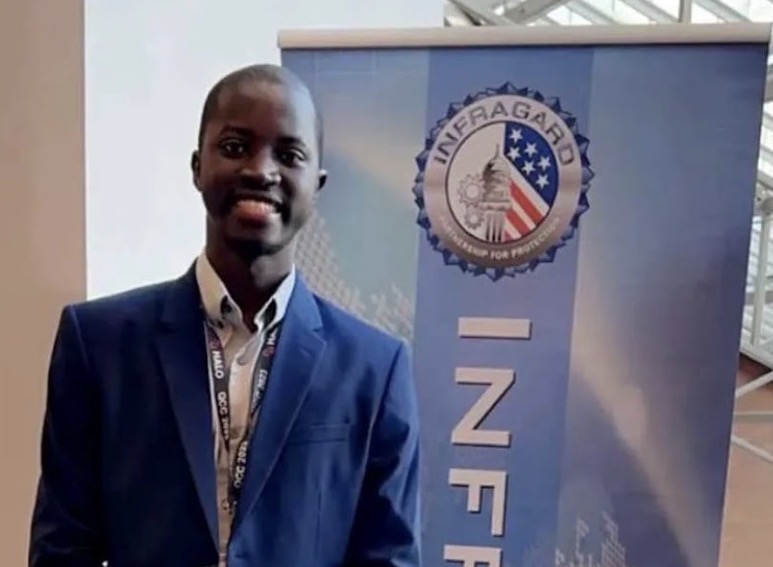
Hamdou Wane — Endpoint & Cloud Security Consultant
Microsoft Intune, Defender for Endpoint, and Windows Autopilot — engineered for banks, aviation, and enterprises that cannot afford a breach. 7+ years. MD-102 certified, CompTIA Security+, InfraGard member.
07+
Years in the field
03
Regulated industries
05
Published technical deep dives
[ 01 — Publications ]
Endpoint engineering experience across banking, aviation, insurance, manufacturing, and software.
Cincinnati, OH
Available for consulting
[ 02 — The Consultant ]
Seven years of endpoint engineering across regulated industries — banking, insurance, manufacturing, and enterprise software. Currently building endpoint and identity infrastructure at a major insurance carrier, with prior work spanning fleet management, zero-touch provisioning, and compliance-driven device policy.
Through ZTrust Africa, Hamdou brings enterprise-grade Microsoft Intune, Defender, and Autopilot expertise to organizations that need a fleet that deploys itself, defends itself, and passes every audit.
[ 03 — Capabilities ]
Full mobile device and application management. Enrollment strategy, compliance policies, configuration profiles, and Conditional Access policy design that survives audit.
Deployment, tuning, and response playbooks for Microsoft Defender. Attack surface reduction, EDR onboarding, and alert fatigue eliminated.
Zero-touch provisioning at fleet scale. From hardware hash to productive device without a technician touching it. Ships direct to the user, no imaging infrastructure required.
Zero-trust architecture across Microsoft 365 and Azure. Identity hardening, tenant baselines, and security posture reviews for regulated environments.
[ 04 — Field Record ]
Hardened and managed endpoint fleets inside a regulated banking environment. Built compliance-driven Intune policies where an unmanaged device is not an inconvenience — it is an audit finding.

Built Intune site profiles for the Shopfloor 2.0 migration across roughly 100 manufacturing sites and 10,000 devices — device configuration policies, dynamic groups, PowerShell scripting, and application packaging in a Government Cloud tenant.

Intune, Configuration Manager, Autopilot, and Entra ID at enterprise scale. Windows 11 feature-update rollout, compliance policy design, and endpoint hardening in a regulated insurance environment.
Endpoint and identity engineering across a distributed manufacturing environment of 3,000+ devices. Configuration Manager, Intune, and Entra ID integration.
Identity and access administration for a global software organization — device management and endpoint operations.
[ 05 — Credentials ]
MD-102
Microsoft 365 Certified: Endpoint Administrator Associate
CompTIA Security+
Credly verified
InfraGard
Member, Cincinnati chapter
7+ Years
Regulated-industry field experience
[ Verified Credentials ]
[ 06 — How We Work ]
Tenant assessment against a Zero Trust baseline, prioritized findings, and a remediation roadmap.
Intune, Autopilot, or Conditional Access build-out — documented and handed over to your team.
Architecture review, escalation support, and policy design as you scale.
Every engagement is scoped on a call — book yours below.
[ 07 — Engage ]
Hamdou Wane
Principal Consultant — ZTrust Africa